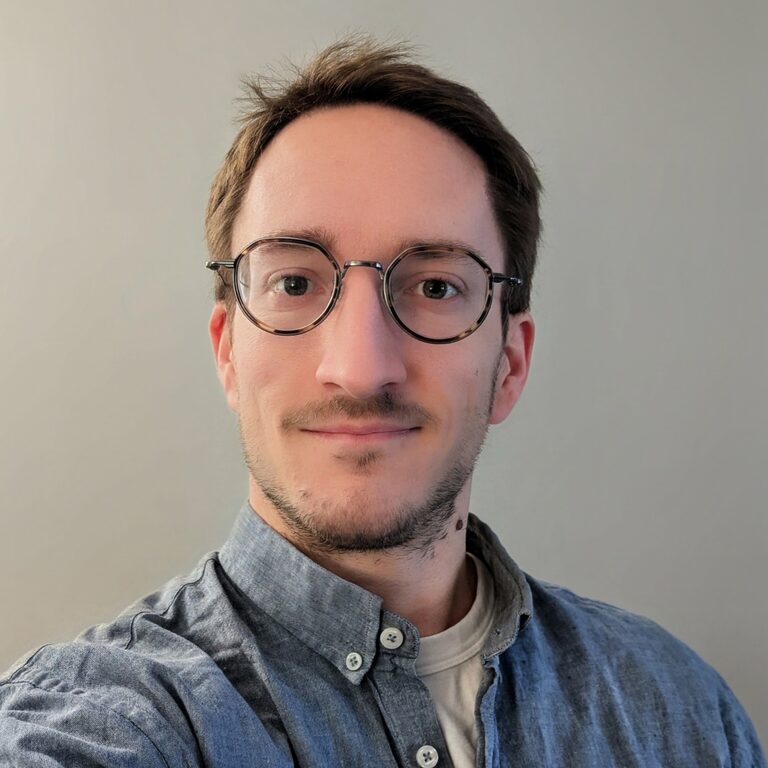
Rémy Beaufils
Senior Cybersecurity Consultant
Compliance, governance and security project leadership
Over 10 years of experience, including more than 6 years in consulting firms. Former Deputy CISO and manager of an audit and pentest team.
I help regulated companies (banking, insurance, healthcare, industry) pass their audits and achieve compliance (DORA, VAIT, ISO 27001, GDPR), leading cross-functional projects and advising security leadership.
- Available immediately
- Remote across Europe
- Paris hybrid
- Le Mans area: up to 100% on site
About Me
Senior cybersecurity consultant with over 10 years of experience, including more than 6 years in consulting firms.
Former Deputy CISO and manager of an audit and pentest team.
I help regulated companies (banking, insurance, healthcare, industry) pass their audits and achieve compliance (DORA, VAIT, ISO 27001, GDPR), leading cross-functional projects and advising security leadership.
What I bring
Governance, risk and compliance
- DORA, ISO/IEC 27001, GDPR
- Risk management and third-party risk management (TPRM)
- Business continuity (BCP/DRP)
- Incident and crisis management
- Security audit
Both a regulatory and a technical perspective: my offensive and engineering background (pentest, code audit, AWS, DevSecOps, IAM, PKI) lets me verify that a control actually works, not just that it is documented.
For whom: regulated organisations, directly or through IT services firms and consultancies, on a time-and-materials basis; open to permanent positions.
Quick Facts
Current role
Availability
- Available immediately
- Remote across Europe
- Paris hybrid
- Le Mans area (Laval, Angers, Rennes): up to 100% on site
Certifications
- COBIT Foundation (2019)
- ISO 27001:2013 Lead Auditor, LSTI (2017, expired)
- In progress: ISO/IEC 27001:2022 Lead Implementer, EBIOS RM
Education
- Master of Computer Science, Supinfo Lyon (2015)
- Computer Science Degree, Epitech Lyon (2013)
Languages
Key achievements
Compliance, audits and risk
No major non-compliance
BaFin audit (German financial regulator), two acquisition audits (due diligence) and an internal Allianz Direct audit passed with no significant security finding (Luko)DORA: 4 of 5 pillars
DORA readiness (Allianz Direct) on 4 of 5 pillars: led encryption and segmentation, co-led incident management; contributed to the assessment of about 150 Luko suppliersSignificantly lower external risk level
External security rating of an international industrial conglomerate raised from C- to A (domains, exposed infrastructure)
Leadership and technical delivery
Staffing above targets
Team of 3 to 5 consultants: utilisation rate (TACE) of 95% against an 80% target (digital.security)Many tenders won
About 50 pentest engagements won; vulnerability management service centre won through a tender for a medical device manufacturer (a dozen product lines)Complex PKI & IAM project management
End-to-end PKI and key ceremonies for an investment firm; IAM for populations of 500 to 20,000 identities
Skills
Both a regulatory and a technical perspective: verifying that a control actually works, not just that it is documented.
Governance, risk and compliance (GRC)
Translating regulatory requirements into concrete security measures.
- RGPD / GDPR
- DORA
- ISO 27001
- VAIT
- COBIT
- Security policies
- Risk assessment and management
- Gap analysis
- Regulatory audits and due diligence
Resilience, incidents and third parties
Preparing the organisation for incidents and managing third-party risk.
- Incident and crisis management
- Third-party risk management (TPRM)
- Business continuity (BCP/DRP)
- Resilience testing: chaos engineering, crisis exercises
- Pentest programme
Project management, leadership and enablement
Leading cross-functional security projects and building team skills.
- Cross-team project management
- Multi-team coordination
- Team management
- Budget and planning
- Pre-sales and recruitment
- Awareness and training
- Security Champions
- Knowledge transfer
Technical audit and vulnerabilities
Testing controls under real-world conditions.
- Penetration testing
- Code audit
- Vulnerability management and bug bounty
- Forensic
Cloud security and DevSecOps
Building security into every stage of the software development lifecycle.
- Cloud security (AWS)
- DevSecOps
- CI/CD pipeline security
- Development (Python, Java)
Identity, PKI and cryptography
Protecting identities, access and cryptographic assets.
- IAM
- PKI and HSM
- Encryption and key management
- Active Directory
Experience
Over 10 years of experience, including more than 6 years in consulting firms. Former Deputy CISO and manager of an audit and pentest team.
Nykteo Consulting
Independent cybersecurity consultant
Cybersecurity consulting company (SASU).
Key Achievements
- Founded the company (SASU) and its advisory offer: governance and compliance, DevSecOps and cloud security, IAM and PKI, security audit
Allianz Direct
Deputy CISO
Insurance company, division dedicated to direct online sales.
Key Achievements
- DORA readiness: led the encryption and network segmentation workstreams; contributed to asset classification, policies, BCP/DRP and backup testing
- Incident management (co-owner): qualification, classification, response procedures; resilience testing: chaos engineering, pentest programme, crisis exercises
- Third-party risk: contributed to the assessment of about 150 Luko suppliers and to impact analyses for provider changes
- Secure transfer of Luko’s assets; coordinated four security teams; supported the CISO
Key Achievements
- Secured the AWS environment; data encryption and key management; owner of security incident management
- 4 penetration tests: findings follow-up, support for developers and verification of fixes
- Led, with engineering teams, the integration of security tooling into CI/CD pipelines
- Created and ran the Security Champions programme (about 10 people) and phishing simulations: failure rate down from over 40% to under 10%
- GDPR and VAIT compliance and audits, coordinating with legal, engineering and management: BaFin audit, two potential buyers’ due diligences with no significant security finding, internal Allianz Direct audit after the buyout
digital.security / Atos
Audit and Pentest Manager (AURA region)
Cybersecurity services company, acquired by Atos.
Audit and Pentest Manager (AURA region)
Key Achievements
- Managed a regional team of 3 to 5 consultants and the unit’s budget; utilisation rate (TACE) of about 95% against a target of 80%
- About 50 pentest engagements won; won the tender for a continuous vulnerability management service centre for a medical equipment manufacturer (a dozen product lines, 2 sites, mostly remote)
- Technical pre-sales, recruitment and project planning
Security Consultant
Key Achievements
- Audits, penetration tests and forensic data analysis
- Python tool development; bug bounty programme management
- Owner of the DevSecOps offer: support for DevSecOps practices and code scanning tools; installed and initially configured Checkmarx in an internal service centre
- Led project teams of 3 to 5 people
Exakis
Security Consultant
Security-focused brand, from consulting to solution integration.
Key Achievements
- IAM consulting and integration (populations of 500 to 20,000 identities), end-to-end PKI and Active Directory; GDPR consulting
- Implemented smart-card and network HSMs; HSM and CA key ceremonies, including for an investment firm
- Led project teams of 3 to 5 people; bug bounty programme management
- Short assignments for insurance, healthcare, finance and staffing clients (PKI, IAM, governance audit)
E-Sublet
CTO and Co-Founder
Online housing sublet service with legal support.
Key Achievements
- Designed the platform architecture and fraud detection mechanisms (identity, payment)
- Technical management, commercial strategy and fundraising; run alongside my studies and then Exakis
Tech Stack
Key technologies used on assignments, in support of controls verified in the field.
Cloud and automation
DevSecOps and code analysis
Audit and penetration testing
Identity and cryptography
Third-party risk
Development
Let's Connect
 Book a slot on Calendly
Send me a message
Contact Information
Time-and-materials engagement (directly or through an IT services firm or consultancy), permanent position or compliance project: email me or book a slot.
To limit spam, I do not publish my phone number, but I can share it if needed after a first contact.